
Key takeaways
- On October 29, 2026, an attacker moved approximately USD 6.36 billion out of Binance wallets on ten blockchains, most of it in about 20 minutes starting at 20:05 UTC. That makes this the largest crypto theft on record, about four times the USD 1.5 billion Bybit hack of February 2025. Binance has confirmed a security incident and suspended withdrawals on several networks.
- TRM attributes the attack to TraderTraitor, North Korea’s elite hacking unit, based on robust on and off-chain intelligence. We make this judgment with high confidence. TRM is tracking the funds and alerting partners through the Beacon Network.
- On Ethereum, the attacker used an EIP-7702 delegation to turn a Binance hot wallet into a sweeper it controlled, with 50 pre-signed authorizations prepared in advance. In the same window, Binance wallets on the other nine chains sent funds to the attacker through ordinary signed transfers. In TRM's assessment, this points to a compromise of Binance's hot wallet signing infrastructure.
- Tether, Circle, Ripple and World Liberty Financial froze about USD 2.67 billion in stablecoins, and Arbitrum's Security Council froze 8,426 ETH and 74.6 million ARB on its network, for a total of roughly USD 2.7 billion. The attacker raced the freezes by selling USDT to market makers and borrowing ETH against USDT on Aave. It now holds more than 420,000 ETH and 18,270 BTC, about USD 2.4 billion in assets beyond any issuer's reach.
What happened
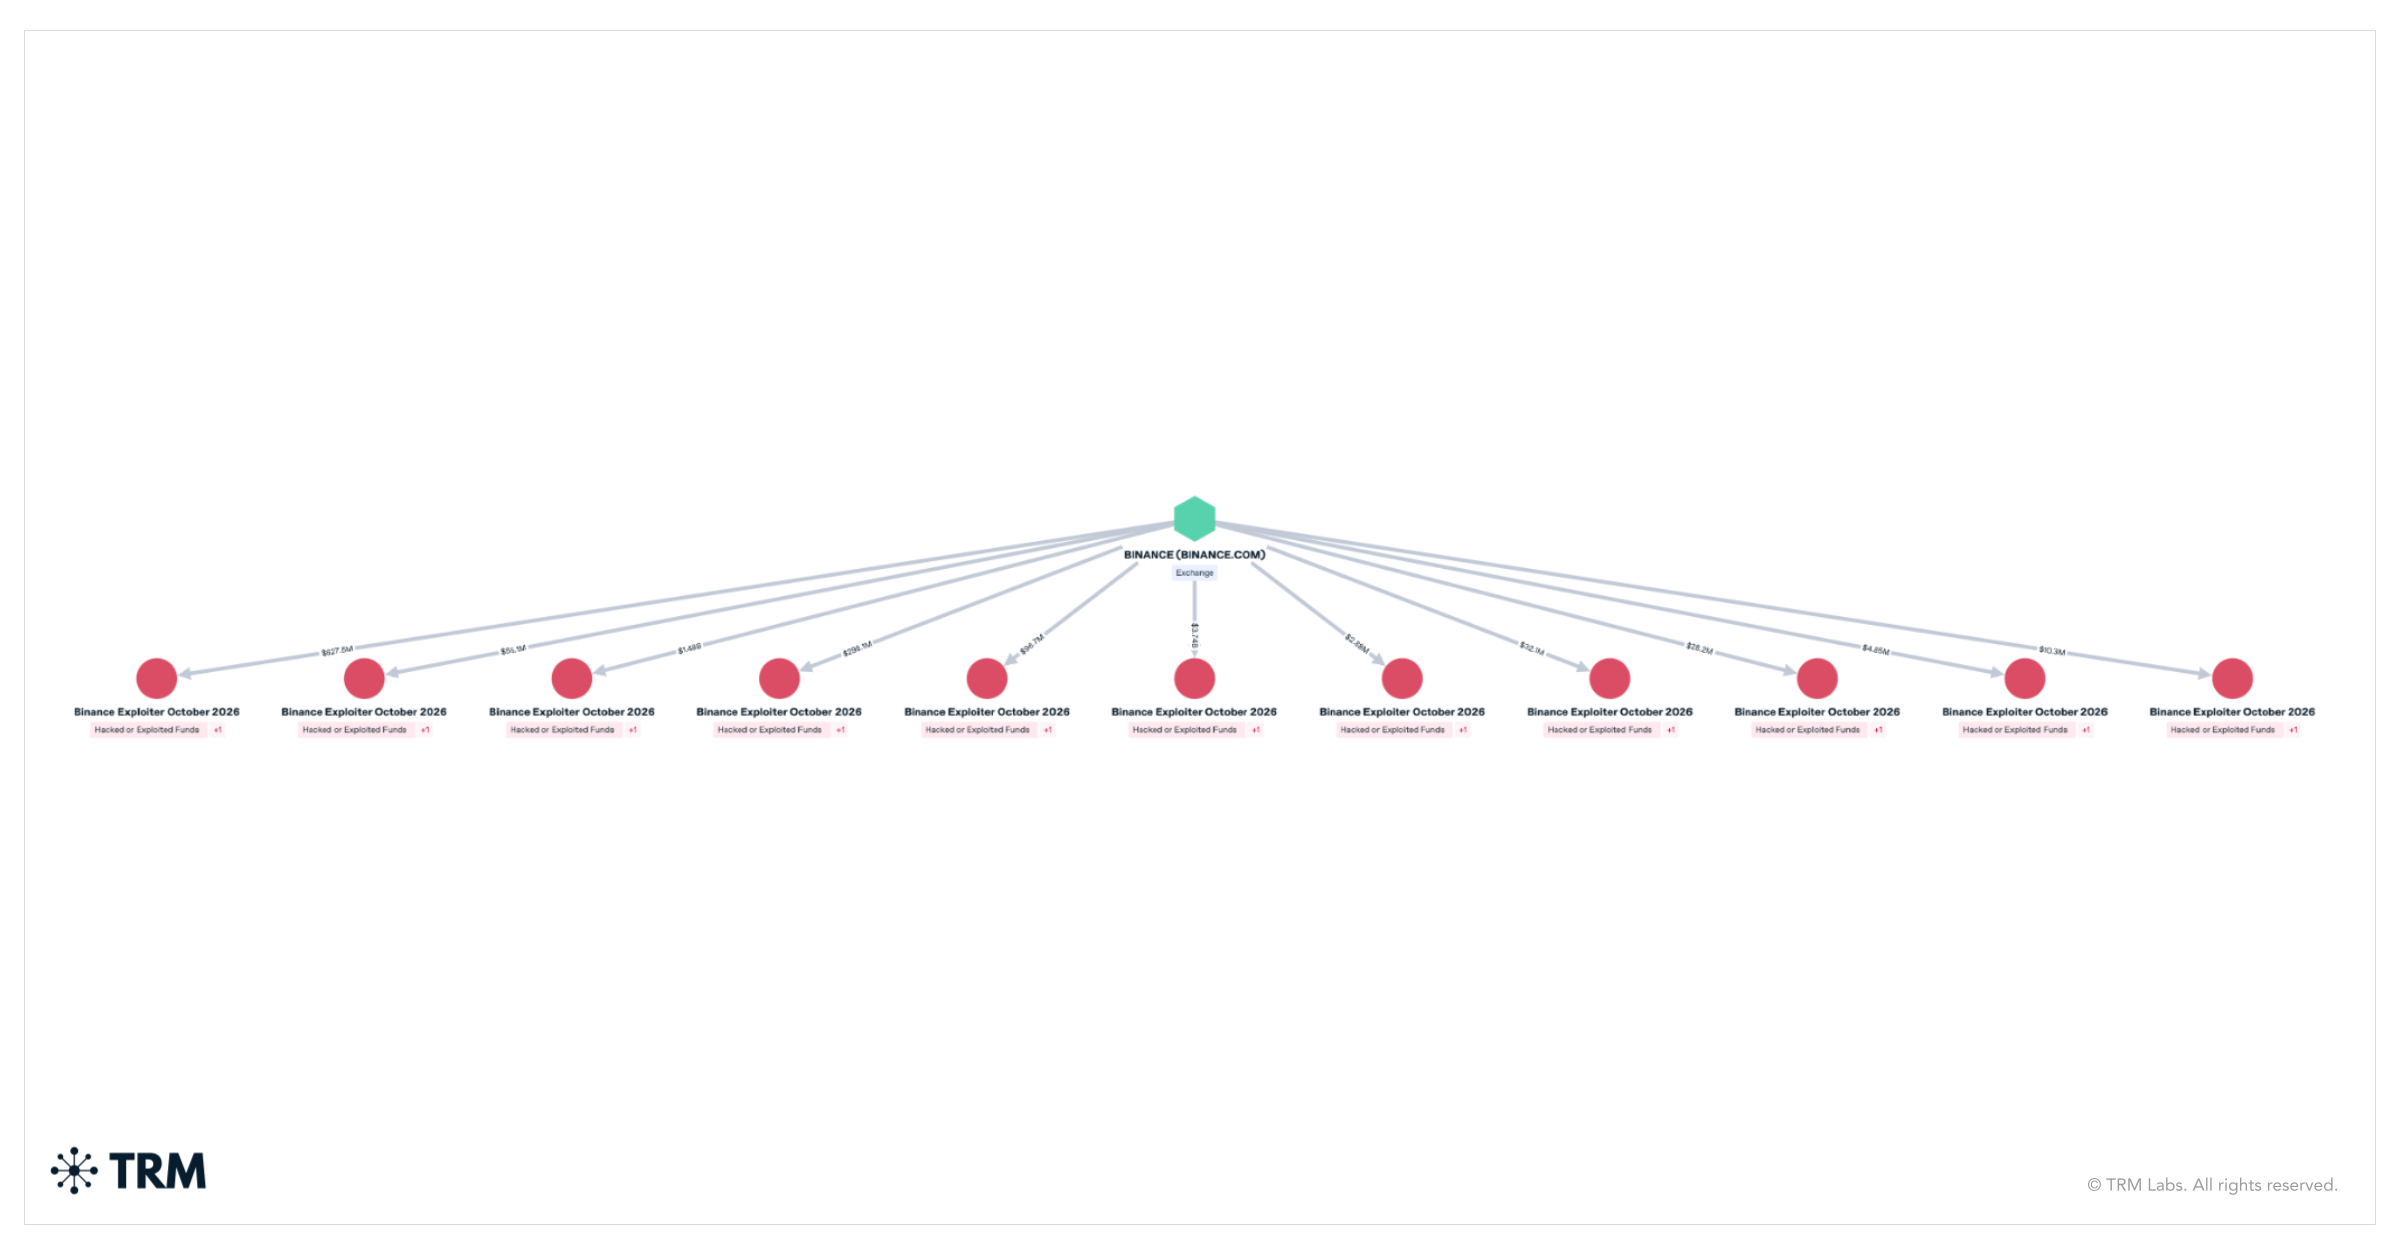
On the evening of October 29, billions of dollars in crypto began leaving wallets belonging to Binance, the world's largest cryptocurrency exchange. Within minutes, Binance wallets on the XRP Ledger, Ethereum, Bitcoin, Tron, Solana and four other networks had sent their balances to addresses controlled by a single attacker. A second wave around 23:05 UTC reached Binance wallets on Avalanche and Polygon.
Binance said it was investigating a potential security issue, then said it had temporarily suspended withdrawals on multiple networks as a precaution. Binance has said user funds are safe. The story is still developing, and the figures here reflect what TRM saw onchain as of October 30 at 00:30 UTC.
Who is behind it
TRM attributes this attack to TraderTraitor, North Korea’s premier hacking unit. We base this assessment on robust on and off-chain intelligence sources. The FBI named the same group as responsible for the USD 1.5 billion Bybit hack in February 2025. Several features of this attack match earlier North Korea-linked heists, including the Bybit hack and the KelpDAO hack in April 2026: small Tornado Cash withdrawals funding an operator wallet, staging that began well before the theft, and signatures obtained in advance then executed in one burst. The laundering observed so far, built on large swaps through market makers and lending protocols, differs from the bridge-heavy pattern that followed Bybit. TRM will share further findings as the investigation develops.
How much was taken
TRM traced every transfer from Binance-attributed wallets to attacker-controlled addresses across ten blockchains. Valuing each transfer at the price of the asset at the moment it was taken, the total is approximately USD 6.36 billion. At current prices, the same assets are worth about USD 6.23 billion.
Ethereum accounts for about USD 3.79 billion. That includes 200,630 ETH and 185 other tokens, among them 1.875 billion USDT, 823 million USDC and 88.5 million RLUSD. Bitcoin outflows total 18,270 BTC, about USD 1.47 billion. Tron outflows total 612.7 million USDT and 46.4 million TRX, about USD 628 million. The XRP Ledger lost 233.46 million XRP, about USD 296 million. Solana outflows total 970,500 SOL, about USD 96 million. Arbitrum, Optimism and Base combine to about USD 39 million, including 74.6 million ARB taken on Arbitrum. Avalanche outflows total about USD 28 million, and Polygon outflows total about USD 10 million.
How the attack unfolded
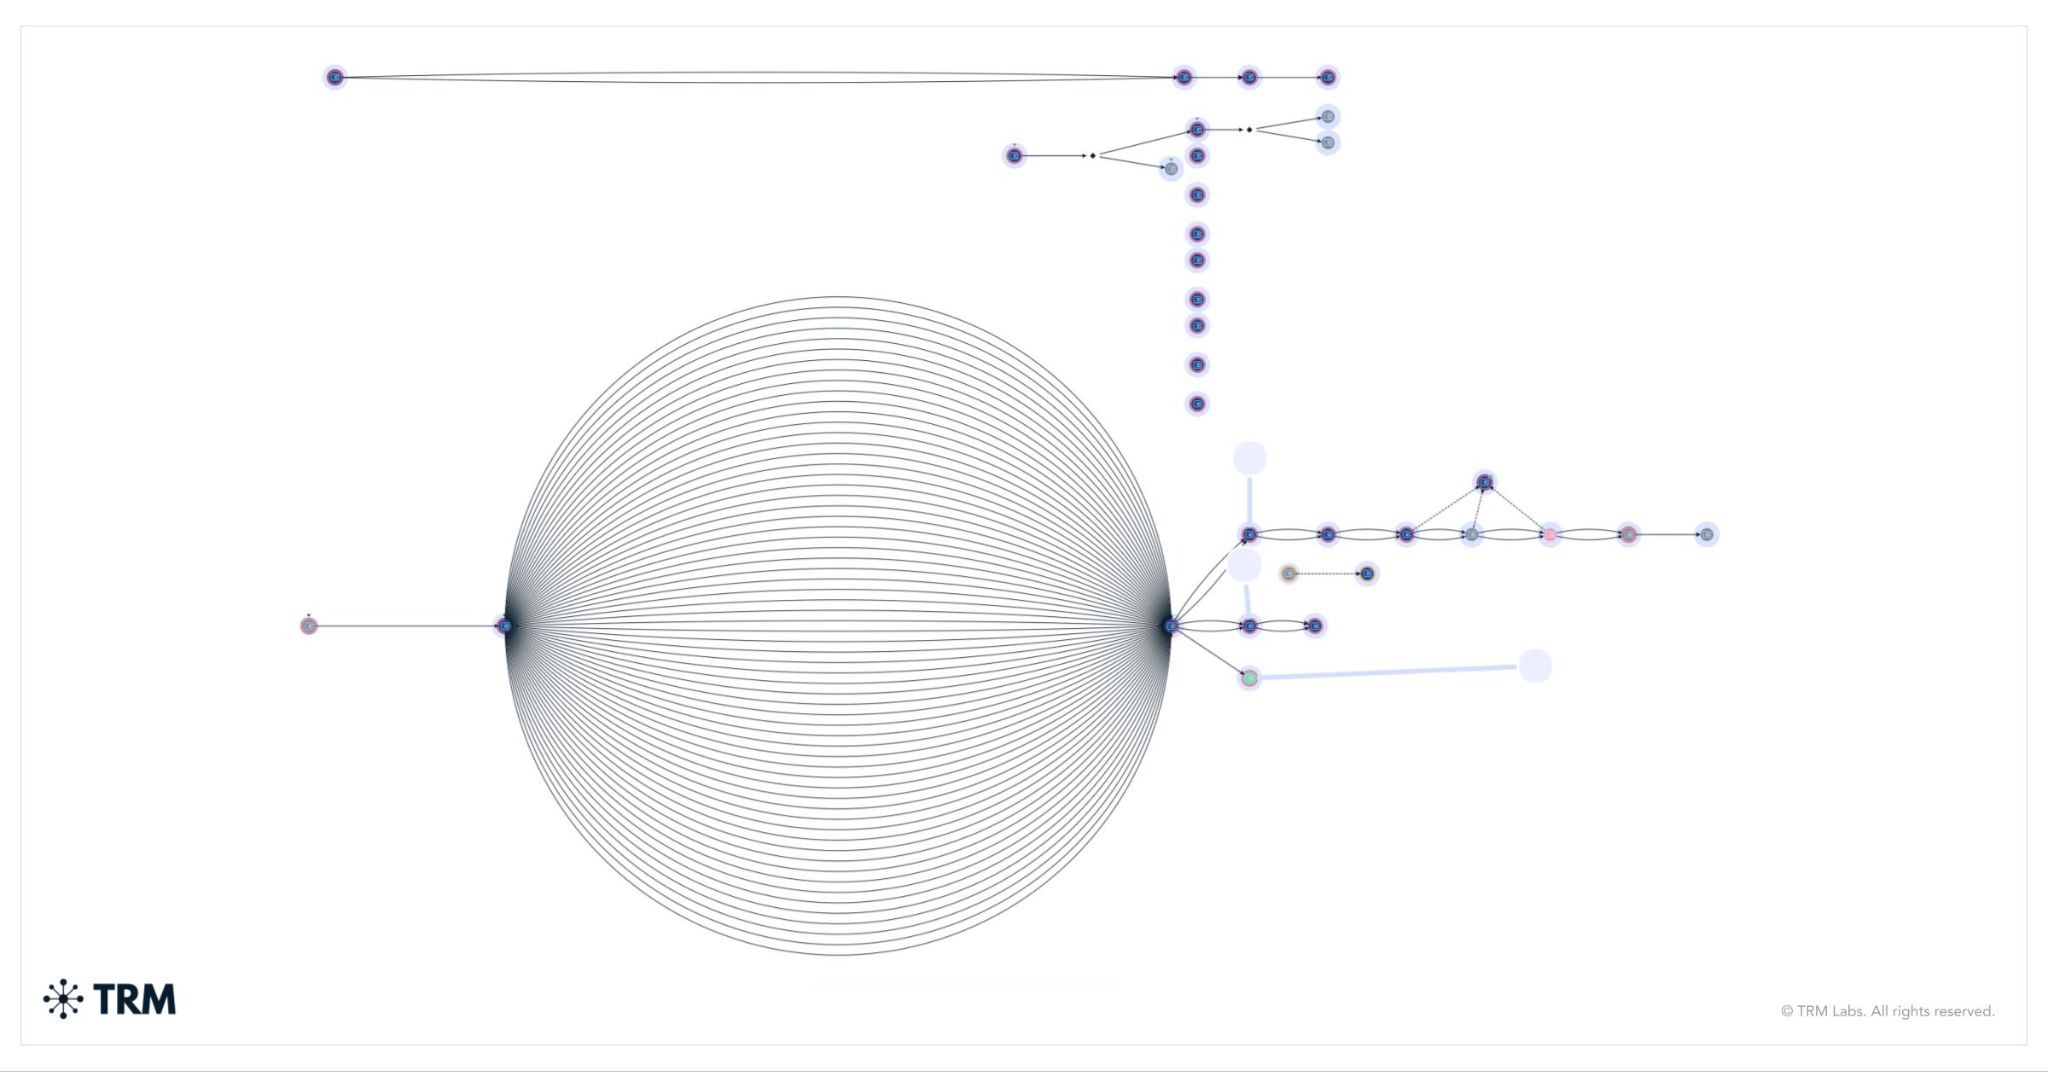
Preparation began at least 36 hours before the theft. The attacker's operator wallet received three small withdrawals from Tornado Cash, a service that obscures where crypto comes from, starting the morning of October 28. Early on October 29, the operator deployed a first piece of code for the attack and tested it on two wallets. Later that day, it rehearsed the final version on a third wallet, then routed the test funds back to itself. Four hours after that rehearsal, the same code was installed on a Binance hot wallet.
The first theft of the night came on the XRP Ledger. Between 20:05 and 20:09 UTC, five Binance wallets sent 233.46 million XRP to a single attacker address, leaving each wallet with only its minimum balance. That XRP has remained in place since. Binance wallets on Solana and Optimism followed shortly after 20:10 UTC. At 20:20 UTC, a Binance Bitcoin hot wallet sent 18,270 BTC to an attacker address, which began splitting the funds into round 1,000 BTC and 100 BTC pieces inside the same block. That technique, called a peel chain, makes funds harder to follow. Within two minutes, a Binance hot wallet on Tron sent 612.7 million USDT and 46.4 million TRX to the attacker.
How the attacker took over a Binance hot wallet
A hot wallet is a wallet connected to the internet that an exchange uses to process customer withdrawals. The Ethereum hot wallet in this case is one of the best-known Binance wallets.
EIP-7702, introduced in Ethereum's Pectra upgrade in May 2025, allows an ordinary wallet to hand control of its behavior to a smart contract by signing an authorization. From then on, every call to the wallet runs that contract's code, and the arrangement stays in place until the wallet signs a new one.
At 20:20 UTC, the operator submitted a single transaction containing 50 authorizations. Each was signed by the Binance hot wallet, and each pointed it to a sweeper contract that accepts instructions only from the operator. Every wallet keeps a running count of its transactions, called a nonce, and an authorization works only at the count the wallet has reached at the moment it executes. The Binance hot wallet processes a steady flow of withdrawals, so its count keeps moving forward. By preparing signatures for 50 consecutive counts, the attacker guaranteed that one would still be valid when the transaction executed. One matched, which was all the attacker needed. The signatures were produced in advance as a batch.
Three minutes and 24 seconds after the delegation, the operator instructed the Binance hot wallet to send its entire balance to an attacker-controlled address. That single transaction moved 167,464 ETH and 63 tokens, including 1.615 billion USDT.
The delegation remained in place. As new funds reached the Binance hot wallet, the operator swept them again at 20:41, 20:59, 21:04, 21:44, 22:39 and 23:56 UTC. The wallet also served as the executor of a separate Binance smart account, which gave the attacker the ability to pull 823 million USDC from it. Circle froze that USDC shortly afterward.
Evidence points to Binance's signing infrastructure
Early indicators on the Ethereum activity suggested the attacker had phished the authorizations. That explanation covers Ethereum and leaves the other chains unexplained. In the same window, five Binance wallets on the XRP Ledger, Binance wallets on Arbitrum, Avalanche, Optimism and Base, a Binance Bitcoin hot wallet, a Binance hot wallet on Tron and a Binance wallet on Solana sent funds to the attacker through standard signed transfers. Another Binance hot wallet on Ethereum sent 28,006 ETH, 55.7 million USDT and 25.9 million RLUSD the same way, without any delegation. About two and a half hours later, at 23:05 UTC, Binance wallets on Avalanche and Polygon followed.
These wallets use different chains, key types and signing schemes. All of them produced valid signatures for the attacker within about half an hour. In TRM's assessment, the most likely explanation is that the attacker gained the ability to make Binance's hot wallet signing system sign transactions of its choosing across chains. The batch of 50 pre-signed authorizations suggests the access may have been limited in time, or that signatures had to be requested through a system. Binance has yet to publish a root cause.
Stablecoin freezes and conversion
Stablecoin issuers moved quickly, and the freezes kept spreading through the night. Binance said at 23:35 UTC that the verified total frozen had reached USD 2.54 billion. Including later freezes, TRM counts about USD 2.7 billion frozen onchain as of 00:30 UTC:
- Tether, about 1.77 billion USDT. Tether froze 971.1 million USDT in the main receiving wallet at 21:01 UTC, 37 minutes after the main sweep. Later sweeps landed in the frozen wallet, which now holds 1.175 billion USDT. Tether also froze 205 million USDT in two other attacker wallets on Ethereum, 378.7 million USDT in two attacker wallets on Tron and 8.4 million USDt on Avalanche. Another 6.2 million USDT0 on Polygon is frozen as well.
- Circle, about 825 million USDC. Circle froze the 823 million USDC in the main receiving wallet at 21:04 UTC, in coordination with law enforcement. It later froze 1.56 million USDC that the attacker had swapped from AVAX and bridged from Avalanche to Ethereum.
- Ripple, 40.5 million RLUSD. Ripple froze the wallet holding the stolen RLUSD at 22:01 UTC, with 40.5 million of the 88.5 million RLUSD still inside. It also froze RLUSD in the compromised Binance hot wallet, so new deposits could not be swept. Binance co-CEO Yi He said Ripple helped stop about USD 200 million from moving; TRM has confirmed the 40.5 million RLUSD freeze onchain.
- World Liberty Financial, 27.8 million USD1. World Liberty Financial froze the 27.8 million USD1 in the main receiving wallet at 22:10 UTC, and froze USD1 in the compromised Binance hot wallet at 22:26 UTC.
- Arbitrum Security Council, 8,426 ETH and 74.6 million ARB. Arbitrum's Security Council is a group that can take emergency action on the Arbitrum network. At 00:08 UTC, it used those powers to force two transfers out of the attacker's wallet on Arbitrum, moving 8,426 ETH and 74.6 million ARB, about USD 30 million, out of the attacker's reach.
During the first hours, the attacker converted freezable stablecoins into assets beyond any issuer's reach, at steep cost. About 325 million USDT was sold to professional fillers and market makers through UniswapX and other intent-based contracts in exchange for about 122,300 ETH. That implies a price near USD 2,650 per ETH when ETH traded around USD 2,300 to 2,350, a discount of more than 10%. The remaining 175 million USDT from that batch was frozen.
A second attacker wallet supplied 60 million USDT to the lending protocol Aave and borrowed about 19,760 ETH against it, after which Aave froze the affected markets. On Tron, 300 million USDT moved to a wallet that began supplying it to the JustLend lending protocol. A further 200 million USDT moved through a chain of hop wallets that swapped it on Uniswap, and 30 million USDT from that chain was frozen. The 88.5 million RLUSD passed through two hops to a wallet that sold 48 million of it through decentralized exchanges between 21:42 and 22:01 UTC, until Ripple froze the remaining 40.5 million.
With the ETH consolidated in a few wallets and the 18,270 BTC moving through the peel chain, the attacker controls about USD 2.4 billion in assets beyond any issuer's reach. Based on previous large thefts, TRM expects the next stage to involve cross-chain bridges, swap services and over-the-counter brokers. TRM is monitoring the peel chain outputs and the consolidation wallets for those movements.
What exchanges and compliance teams should do now
Exchanges and compliance teams should screen deposits and counterparties against the attacker addresses TRM has labeled. Funds from the Bitcoin peel chain and the ETH consolidation wallets are likely to reach exchanges, swap services and OTC desks in the coming days.
Treasury teams should monitor Ethereum-compatible wallets for EIP-7702 delegations, which appear as code at an address that should have none. Any such delegation on a treasury wallet should trigger an immediate alert. Teams should keep a tested, pre-approved method for signing a revocation.
Signing policies should reject EIP-7702 authorizations unless they are expected. A request for many authorizations across a range of transaction counts should be treated as an indicator of compromise. Signing infrastructure and approval paths should be separated by chain and wallet tier. In this incident, a single actor obtained valid signatures for wallets on ten chains within hours.
Market makers and solvers should screen counterparties before filling large orders. About 325 million USDT was sold to market makers and solvers by a wallet that had received it from the hack minutes earlier. Real-time address screening would have flagged it.
Frequently asked questions
- What happened to Binance?
On October 29, 2026, an attacker moved approximately USD 6.36 billion out of Binance wallets on ten blockchains, including Ethereum, Bitcoin, Tron, the XRP Ledger, Solana, Arbitrum, Avalanche, Optimism, Base and Polygon. Binance confirmed a security incident and suspended withdrawals on multiple networks.
- Who is behind the Binance hack?
TRM attributes the Binance hack to TraderTraitor, a North Korean state-sponsored hacking group, based on robust onchain and offchain intelligence. The same group was behind the USD 1.5 billion Bybit hack in February 2025.
- What is EIP-7702, and how was it used?
EIP-7702 lets an ordinary Ethereum wallet run a smart contract's code by signing an authorization. The attacker used a pre-signed authorization to make a Binance hot wallet run a sweeper contract that only the attacker could call, then used it to drain the wallet and to keep sweeping new funds that arrived later.
- How much of the stolen crypto has been frozen?
Tether, Circle, Ripple and World Liberty Financial have frozen about USD 2.67 billion in stablecoins, and Arbitrum's Security Council has frozen about USD 30 million in ETH and ARB, roughly USD 2.7 billion in total. The attacker still controls more than 420,000 ETH and 18,270 BTC, worth about USD 2.4 billion, plus smaller amounts on other chains.
- How does this compare to other major hacks?
At about USD 6.36 billion, this is the largest crypto theft on record, about four times the USD 1.5 billion Bybit hack of February 2025. Even after the stablecoin freezes, the amount the attacker still holds exceeds any previous theft.